Cybersecurity for SMEs, clear defense, verifiable results
Your data is not negotiable.
Cyber attacks are expensive for small businesses: data loss, operational downtime, reputation damage. NEXUS AGENCE helps you identify vulnerabilities, harden your defenses, and train your team so everyone understands real risks, no jargon.
Audit in 4–6 weeks · detailed report · priority action plan · follow-up included
Full auditAnalysis of entry points, passwords, backups, access and logs.
Clear reportExecutive summary in plain English, no unnecessary jargon.
Action planPrioritized steps, estimated costs and realistic timelines for each fix.
Team trainingHalf-day workshop: phishing, passwords, backups and best practices.
6-month follow-upPeriodic checks that corrections have been properly implemented.
100% confidentialData covered by professional confidentiality, no third-party sharing.
Three levels of engagement
Every SME has different needs.
You can start small (quick audit) and scale up to more robust protection. The key is identifying your real risks and putting in place what matters for your business.
Quick audit
For an SME wanting a first overview without long-term commitment.
On-site visit, 4 to 6 hours.
Team questionnaire, 30 min.
Summary report with top 5 recommendations.
Q&A after report delivery.
$699 all-in$100 less than IT Cares
All-in price: the amount shown is the total to pay, nothing else is added. NEXUS AGENCE is a small supplier not registered for GST/QST: no tax is charged on this amount (applicable taxes, if any, are extra). Stripe payment fees are already included in the amount shown.
One-time payment. No tax charged (small supplier). Receipt emailed immediately.
Full audit
For an SME wanting to understand all risks and get a real action plan.
Two visits: assessment and debrief, 6 to 8 hours each.
Backup and recovery verification.
Testing of existing security measures.
Detailed report with prioritization and budgets.
Half-day team training workshop.
$1,999 all-in
All-in price: the amount shown is the total to pay, nothing else is added. NEXUS AGENCE is a small supplier not registered for GST/QST: no tax is charged on this amount (applicable taxes, if any, are extra). Stripe payment fees are already included in the amount shown.
One-time payment. No tax charged (small supplier). Receipt emailed immediately.
Premium audit
For a small business that wants ongoing support, not just a report.
Everything the full audit includes.
Three monthly 30-minute follow-up meetings.
Priorities revised at every meeting.
$1,899 all inclusive−$2,100 vs IT Cares
All-inclusive price: the amount shown is the total to pay, nothing else is added. NEXUS AGENCE is a small supplier not registered for GST/QST: no tax is collected on this amount.
One-time payment. No tax charged (small supplier). Receipt emailed immediately.
Ongoing monitoring
For an SME wanting regular vigilance and guided corrections.
Full audit + quick audit every 3 months.
Correction tracking (shared checklist).
Alert if anomalies detected (logs, access).
Quarterly action plan updates.
Annual guided password overhaul.
$499/month all-in
All-in price: the amount shown is the total to pay, nothing else is added. NEXUS AGENCE is a small supplier not registered for GST/QST: no tax is charged on this amount (applicable taxes, if any, are extra). Stripe payment fees are already included in the amount shown.
No commitment, cancel anytime. No tax charged (small supplier).
Remote Blue Team scan, subscription
Proactive remote scan on a fixed monthly subscription: continuous monitoring and a monthly report. Subscription exclusive, never offered one-time.
Proactive remote scan, every month.
Continuous monitoring for the duration of the subscription.
Written monthly report, in clear language.
$29,95/month all-in
All-in price: the amount shown is the total to pay, nothing else is added. NEXUS AGENCE is a small supplier not registered for GST/QST: no tax is charged on this amount (applicable taxes, if any, are extra). Stripe payment fees are already included in the amount shown.
No commitment, cancel anytime. No tax charged (small supplier).
Frequently asked
What SMEs often ask.
How long does an audit take?
Quick audit: 4–6 hours on-site, report in 1 week. Full audit: 2 visits of 6–8 hours each, detailed report in 2 weeks. Ongoing monitoring takes a few hours per quarter.
What's the actual cost?
Quick audit starts at $800. Full audit ranges from $2,000 to $3,500 depending on size. Ongoing monitoring varies from $400 to $500 per month. Prices include report, debrief and implementation advice.
What do you do with my data?
Nothing. Your data stays with you. The audit report is covered by professional confidentiality. NEXUS AGENCE doesn't share it with anyone, doesn't send copies to vendors or insurers, and deletes it after two years.
Do we close during the audit?
No. The audit happens during normal hours. We want to see how things really work. Your team continues their tasks while we observe and ask questions.
Who needs to be there?
At minimum, the IT manager (or whoever handles computers), a manager, and a few team members. Not everyone needs to be present, just enough to understand real practices.
What comes next?
You get a report with a prioritized action plan. NEXUS AGENCE can help implement fixes (web, infrastructure) or recommend a trusted local IT vendor for the rest.
The real landscape
An SME is never too small to be attacked. It is often the most profitable target.
An attacker doesn't pick the largest company: they pick the easiest. Without unique passwords, a tested backup and a response plan, an SME recovers more slowly, and pays more. These are the six scenarios seen most often in Quebec.
Ransomware in an attachment
An invoice, a résumé, a delivery notice: the file looks ordinary and encrypts the files within minutes. The ransom demanded is rarely the real loss, the shutdown is.
CEO fraud
An email impersonates a manager and requests a transfer. The money leaves before anyone calls to double-check. A phone confirmation almost always stops it.
Reused passwords
The same password opens the email, the accounting software and the bank. A leak at any supplier becomes a key to everything else.
Backups never tested
The backup file exists, but nobody has ever tried to restore it. On the day of the incident, it turns out to be incomplete, encrypted, or stored on the same disk as the original.
Compromised supplier or software
The flaw isn't yours: it arrives through an update, a module or a subcontractor. Access granted "just for the trial" stays open for months afterwards.
Staff departures, forgotten access
The email account, the cloud access and the router password stay active after the departure. It isn't malice: it's an oversight, and it costs.
The method
Five steps, from the first call to verifying the fixes.
An audit isn't a report you hand over and forget. It's a short loop: understand, test, explain, fix, re-verify.
Step 130 min
Scoping
A 30-minute call to set the perimeter: number of workstations, servers, business software, key people. Together we decide what is included and what is not.
Step 2D+0 to D+5
Collection
Workstations, accounts, backups, network, email, websites. Collection happens during normal hours, without closing the business, with the people who actually use the tools.
Step 3supervised
Verifications
We test what must be tested, with written authorization and without disrupting operations: restoring a backup, password strength, exposure of remote access.
Step 41 to 2 weeks
Report and debrief
An executive summary in plain language for management, then technical detail for whoever runs IT. Every finding carries its priority, estimated cost and deadline.
Step 5follow-up
Fix and re-verify
A shared checklist tracks every fix, from "to do" to "verified". Corrected items are retested, not just taken on trust.
And thenongoing
Vigilance
Depending on the chosen package, the agency returns each quarter for a quick audit, updates the action plan and flags what has changed in the environment.
The scope
What the audit covers, concretely.
Eight areas are reviewed in every full audit. They cover the essentials of what brings an SME down, and each produces verifiable findings, not impressions.
Identities and passwords
Shared accounts, weak or reused passwords, missing two-factor authentication on email and sensitive access. It's the most common way in.
Backups and restore
Frequency, location, the 3-2-1 rule, encryption and above all a real restore test. A backup never restored is not a backup.
Workstations
System and software updates, active antivirus, administrator accounts kept separate from daily accounts, personal devices connected to the network.
Accounts and permissions
Who has access to what, and who should. Former employees, interns and subcontractors are the ones most often forgotten.
Network and Wi-Fi
Guest network separated from the work network, router password, remote access left open without need, equipment left on defaults.
Email and phishing
Filtering, domain authentication (SPF, DKIM, DMARC), a reporting procedure for the team. Most incidents start with an email.
Websites and hosting
Certificate, CMS updates, administrator accounts, site backups. What the agency hosts, it also checks.
Incident response
Who calls whom, in what order, with which offline numbers. A one-page written plan beats good intentions in a panic.
What the protection covers
Six layers, one promise: nothing passes unseen.
An antivirus alone looks at a file when it opens. Defense in depth watches the perimeter, access, patches, backups and traces, continuously. Here is, concretely, what each layer prevents.
Defense in depth: no single layer is enough, that is by design.
1 · Firewall & perimeter
Only the doors that need to stay open are open, and they are known. What shouldn't be reachable from the Internet no longer is, the first layer, and the cheapest one to set up.
2 · Continuous monitoring
Connections, accounts and services are watched continuously. A repeated attempt, an account waking up at 3 a.m., a new service appearing: it is seen, dated and kept.
3 · Patches & updates
Most successful intrusions exploit a flaw that was patched elsewhere long ago. A patch schedule, applied and verified, closes the most-used door.
4 · Passwords & MFA
A reused password is one key opening many doors. Length is required, reuse is banned, and every sensitive access is backed by a second check.
5 · Law 25 compliance
Map the information, decide how long it is kept, write down who can access it. The law requires written decisions: we make them enforceable, not just signed.
6 · Verified backups
A backup that has never been tested is not a backup. We verify that the copy actually restores, and that ransomware cannot encrypt it along with everything else.
The monitoring report: what was attempted, what was blocked, what was fixed.
Five milestones, in that order. Skipping a step costs you later.
Behind the scenes
The workstation behind every audit.
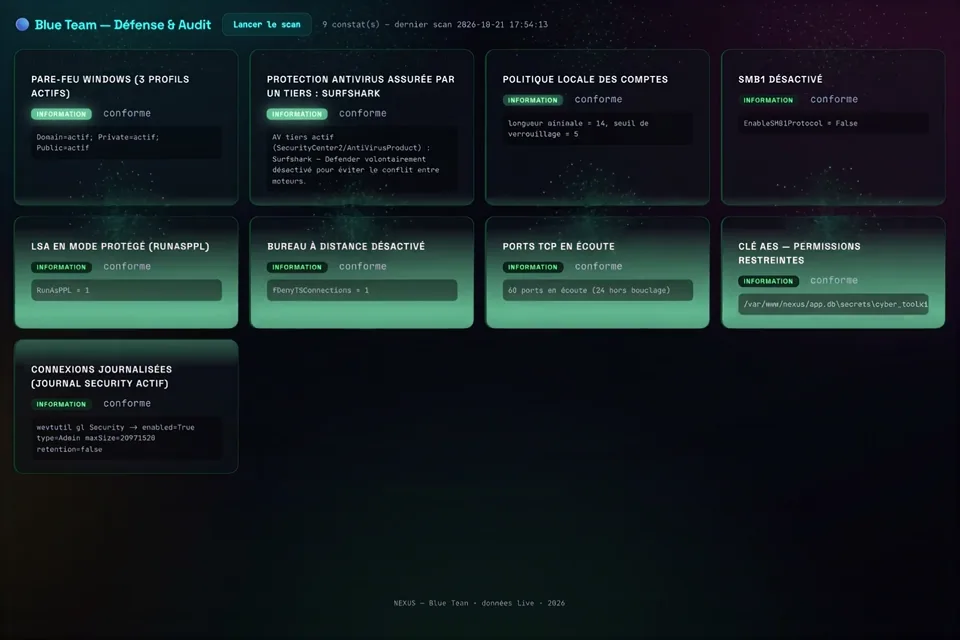
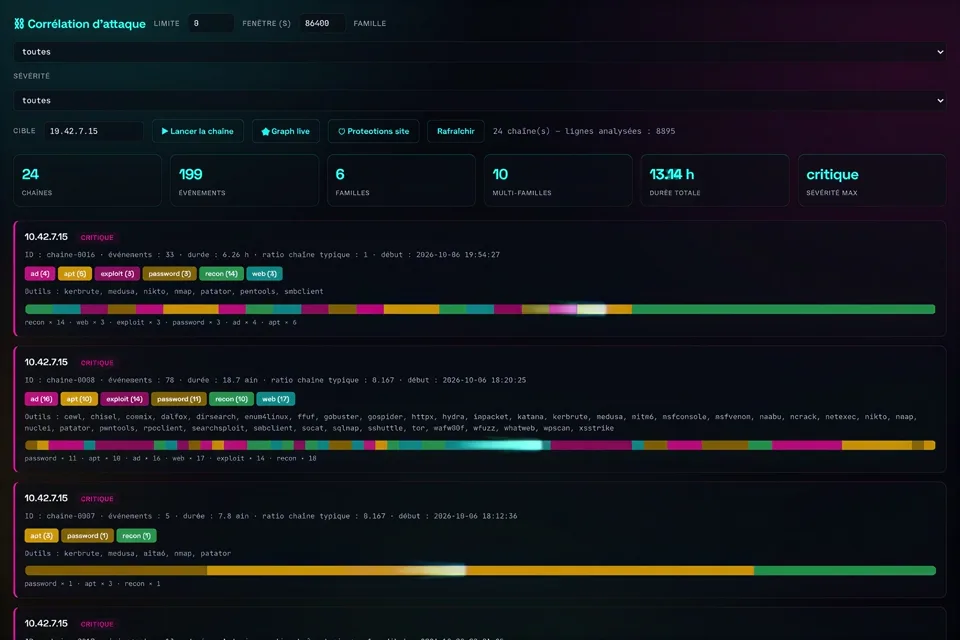
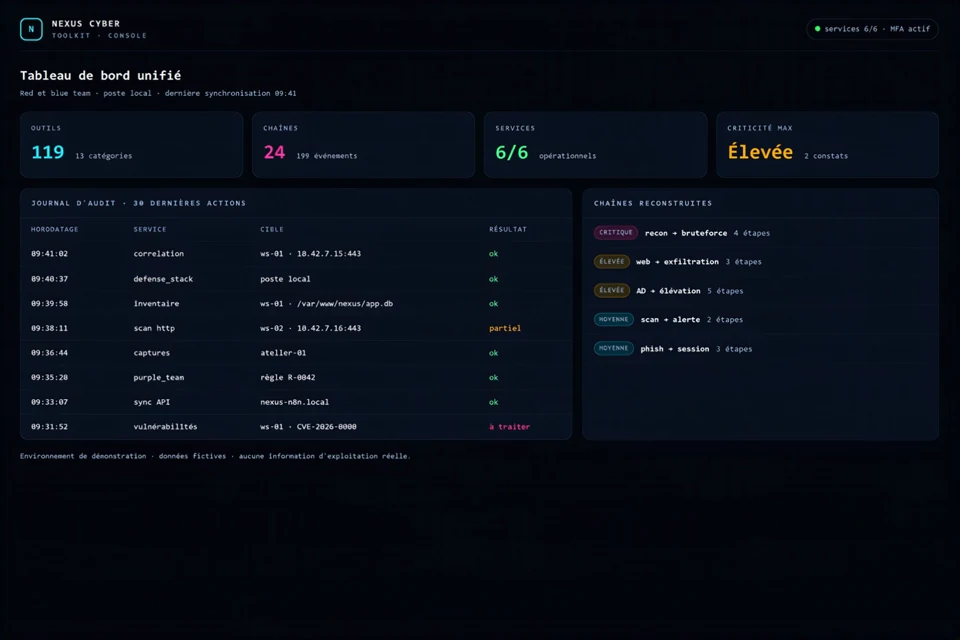
Here, unedited, are the screens actually used during a mission: the tool catalogue, the monitoring station, attack-attempt correlation and the unified dashboard. Addresses, machine names and test identifiers are blurred, a house requirement, not an effect.
The catalogue: every tool grouped by family, run on demand.
The monitoring station: what passes, what doesn't, and the matching fix.
Correlation: several isolated events become one readable attempt.
The unified panel: what is attempted and what is seen, in the same log.
Every capture comes from a local workstation; real addresses and credentials never leave it. The client sees the result, never anyone else's infrastructure.
Compliance · Quebec Law 25
Law 25 doesn't demand perfection. It demands written decisions.
Quebec's Act to modernize legislative provisions on the protection of personal information imposes concrete obligations on businesses. Most are simple, provided they are done before the incident, not after.
Designated officer
Someone must be appointed responsible for the protection of personal information, with contact details published. Often it's the owner, which is perfectly acceptable.
Incident register
Any incident presenting a risk of serious harm must be recorded, and affected people informed. The register is kept calmly, not in an emergency.
Policies and consent
Why each piece of information is collected, how long it is kept, who it is shared with. A clear policy avoids vague promises.
Individuals' rights
Access, correction, withdrawal of consent: these requests must be handled within the prescribed timeframes. A written process beats memory.
NEXUS AGENCE is not a law firm and does not replace legal advice. What the audit provides: a map of the data actually held, the access points that expose it, and the technical fixes that make those decisions enforceable.
The limits
What a NEXUS AGENCE audit does not do.
An honest audit also states what it leaves aside. Here are the four limits, set out in advance, to avoid misunderstandings and billing surprises.
No unauthorized penetration test
Verifications are done with written authorization, on your infrastructure. An intrusive test on a third-party service (host, business software) requires a separate mandate and the supplier's agreement.
No proprietary code review without access
A closed business application cannot be audited from the inside without the supplier's access. In that case, the audit checks configuration, accounts and updates, not the code.
No real-time monitoring without a 24/7 contract
An audit is a dated snapshot. Continuous detection, alerts and uptime reports belong to the 24/7 monitoring service, separate and optional.
No legal advice
Support covers technical and organizational aspects. For an interpretation of Law 25 or contract drafting, the agency refers you to a lawyer, and provides the necessary technical material.
Glossary
The words we use, explained simply.
A report is only worth anything if it is understood. Here are the terms that come up most often, translated into plain language.
Ransomware
Software that encrypts files and demands a ransom to decrypt them. The real defense isn't payment: it's a backup restored successfully.
Two-factor authentication (MFA)
A password plus a second factor (app, key, code). Even if the password leaks, access stays closed. It's the most cost-effective security gain.
Phishing
A message impersonating a trusted sender to get a click, a password or a transfer. Training the team is the best defense.
RPO / RTO
RPO: how much data you accept losing (say 24 h). RTO: how long you accept the business staying down. Two numbers to decide in advance.
Least privilege
Each person holds only the access their work requires, nothing more. A sales account doesn't need to be a network administrator.
The 3-2-1 rule
Three copies of the data, on two different media, one of them off-site. The modern version adds an immutable copy, which ransomware cannot encrypt.
Next steps
Ready to verify your defenses?
Contact NEXUS AGENCE for a free 20-minute discussion. We'll understand your situation and suggest the right audit for you, no pressure.
 Tommy Lafrance's Web AgencyAGENCY • WEB • CYBERSECURITY